Code security

We let an AI agent execute Bash and lived to talk about it — Sarah Sanders, PostHog

We let an AI agent execute Bash and lived to talk about it — Sarah Sanders, PostHog

Sarah Sanders, a context engineer at PostHog, discusses the security implications of building an agentic CLI tool, "The Wizard," which automates developer workflows. She highlights the inherent risks of agents capable of executing commands, labeling it a "malware starter pack," and details how PostHog evolved its security posture from basic allow lists to a sophisticated "defense in depth." Key insights include the principle that "attacks compose, code review doesn't," the discovery of internal supply chain vulnerabilities through the "Context Mill," and the development of "The Warlock," a deterministic scanner using YARA rules. Sanders emphasizes the critical distinction between deterministic enforcement and probabilistic judgment, explaining how an LLM-powered "Triage" layer acts as an adviser (failing closed) rather than a bouncer, preserving the integrity of their security model.
Guide, Verify, Solve — Anirban Chatterjee, Sonar

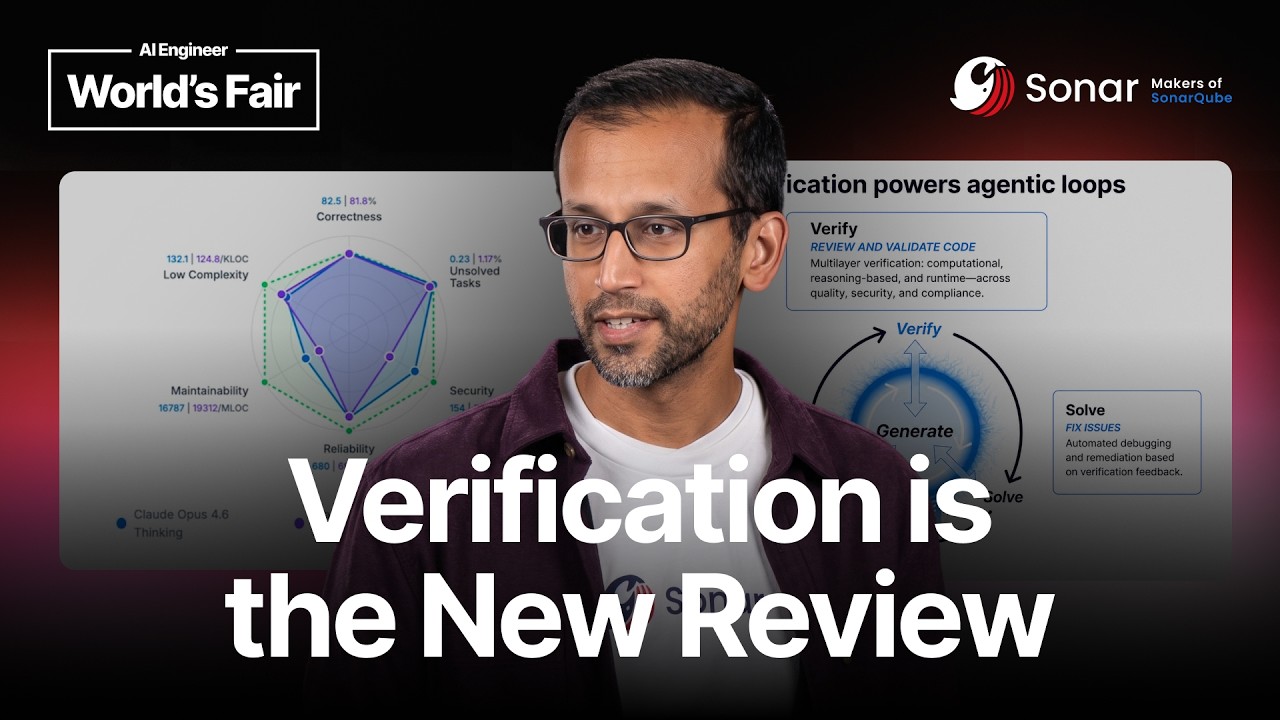
Guide, Verify, Solve — Anirban Chatterjee, Sonar

Anirban Chatterjee discusses the emergence of "verification debt" in AI-driven software development, where AI-generated code introduces persistent quality issues despite initial productivity gains. He proposes a **zero-trust, multi-layered verification** approach, integrating it into an "Agent-Centric Development Cycle" (ACDC) to ensure code quality, security, and compliance by empowering AI agents with real-time feedback and remediation capabilities through tools like SonarQube, Gitarr, and Sonar Vortex.

What is an AI Code Generator? LLM Coding, Productivity, & Risk

What is an AI Code Generator? LLM Coding, Productivity, & Risk

AI code generators leverage LLMs to translate natural language into code, significantly boosting developer productivity and job satisfaction by automating boilerplate and accelerating learning. However, they introduce risks like subtle security vulnerabilities and require rigorous human review. Evaluating tools hinges on trust, demanding features like data provenance, governance, secure deployment, and curated training data for enterprise adoption.