Supply chain attack

Your AI Isn’t the Problem. Your Infrastructure Is. — Jiachen Jiang, Coder

Your AI Isn’t the Problem. Your Infrastructure Is. — Jiachen Jiang, Coder

Jiachen Jiang uses three agent security incidents, the Replit production database deletion, a relayed banking compromise involving Copilot, and the Nx supply chain attack, to argue that prompts cannot enforce boundaries. He maps each incident to six infrastructure controls: environmental separation, short-lived scoped credentials, identity-aligned access, model proxies, sandboxing, and independent audit logs.
OpenAI’s Daybreak and Mistral’s Mythos competitor

OpenAI’s Daybreak and Mistral’s Mythos competitor

This week's podcast delves into the rapidly evolving landscape of AI-powered vulnerability management, discussing OpenAI's Daybreak, Microsoft's MDASH, and Mistral's Mythos competitor. The panel analyzes the measured real-world results of Anthropic's Mythos on the curl project and explores the implications of the notorious Shai-Hulud npm worm going open source.

MCP Security: The Exploit Playbook (And How to Stop Them)

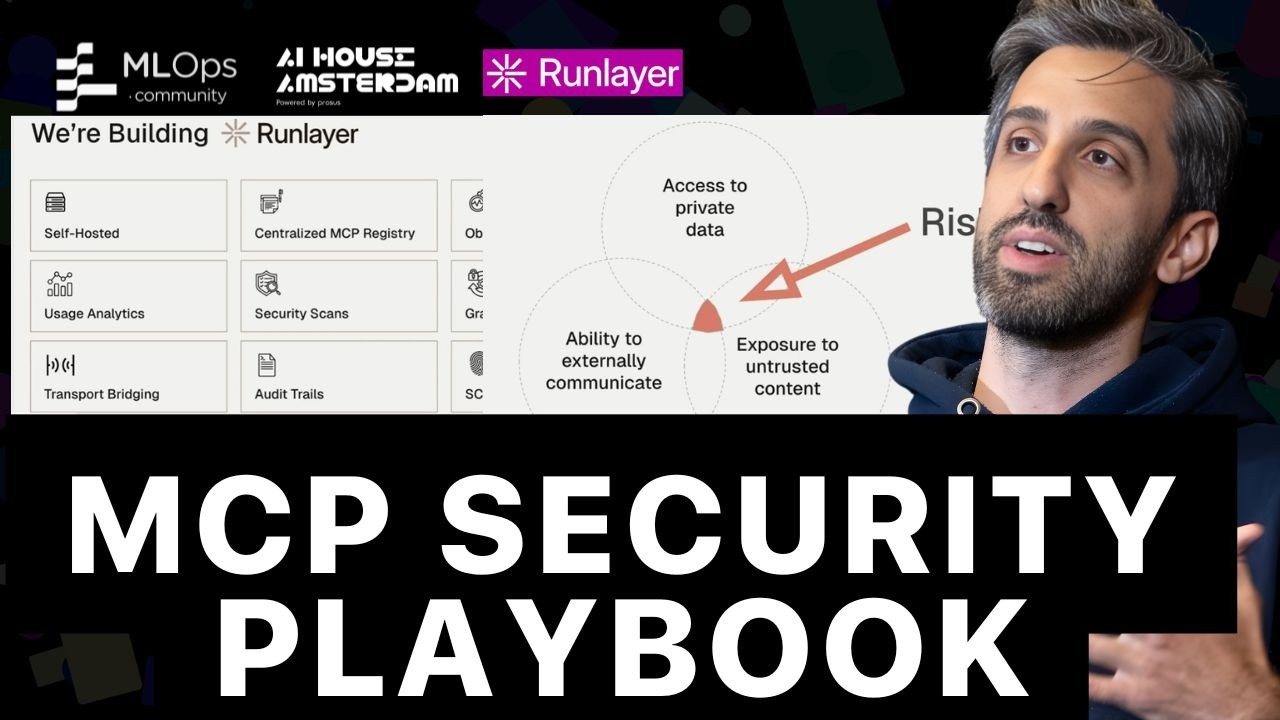
MCP Security: The Exploit Playbook (And How to Stop Them)

Vitor, co-founder of Runlayer and former tech lead for Zapier Agents, provides a deep dive into the security vulnerabilities of the rapidly adopted MCP standard for AI agents. He outlines the primary attack vectors, including sophisticated prompt injections, supply chain attacks like 'rug-pulls', and tool schema manipulation, using real-world exploits as examples. The talk concludes with a multi-layered defensive strategy for users, developers, and enterprises to secure their AI agent deployments.