Policy enforcement

Rebuilding CI for AI-Scale Commit Volume — Gautam Korlam, SonarSource

Rebuilding CI for AI-Scale Commit Volume — Gautam Korlam, SonarSource

A talk on why coding agents shift the bottleneck from code generation to CI, merge queues, review, and approvals, and how to redesign those systems around speed, automated repair, policy enforcement, and auditable records.
Give the Agent a Budget, Not a Token — Sachin Malhotra, Anthropic

Give the Agent a Budget, Not a Token — Sachin Malhotra, Anthropic

Sachin Malhotra's talk outlines a critical framework for safely deploying autonomous agents in production, moving beyond simple token-based access. He introduces 'asymmetric verbs,' refilling 'rate limits,' 'trip wires' for aggregate monitoring, and the 'undo test' as a lens. A central tenet is that infrastructure (via a proxy) must stamp an agent's identity, preventing agents from circumventing controls and ensuring accountability, thus providing a "budget" instead of an unbounded "token."

Policy Enforcement and Tamper-Evident Audit Chains | ​Imran Siddique | MCP Release Party - Seattle

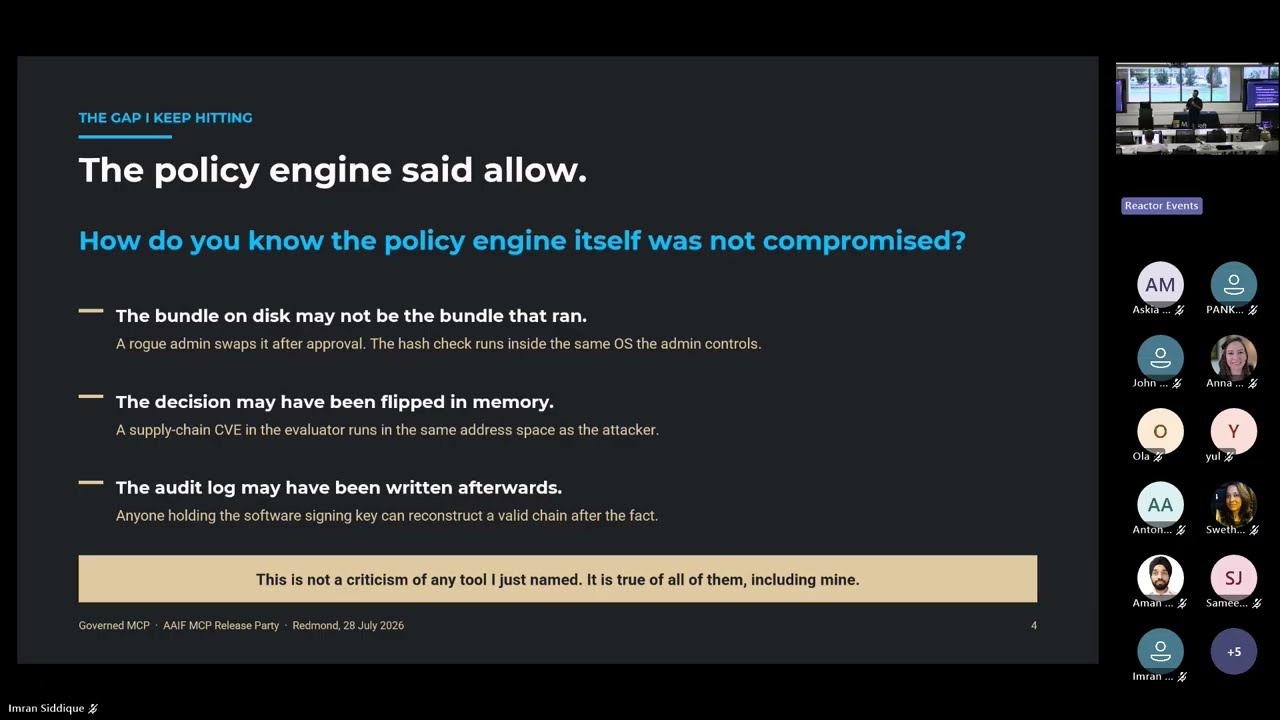
Policy Enforcement and Tamper-Evident Audit Chains | ​Imran Siddique | MCP Release Party - Seattle

Imran Siddique introduces cMCP, an open-source gateway that enhances Modular Control Plane (MCP) servers with policy enforcement and tamper-evident audit trails. It achieves this by running Cedar policy evaluation within Trusted Execution Environments (TEEs), ensuring that agent actions are governed securely and verifiably. The talk delves into the concept of "beyond governance" towards verifiable AI, the 'trace' standard for auditable logging, and the importance of confidential computing for regulated industries.